Guide
How to Prevent AI Cheating in Online Assessments (2026)
A candidate sits a 90-minute remote assessment. The browser is locked. A camera watches their face. By every signal the proctoring software can measure, the session is clean. Underneath it, an invisible overlay is drawing a language model's answers onto the same screen, hidden from the recording. The session ends with zero violations, and an invalid result is certified as valid.
This is the defining failure of remote assessment in 2026, and it is not a bug in any single product. It is a consequence of where the incumbent tools operate. This guide explains the methods that actually prevent AI-assisted cheating, for academic exams, technical hiring interviews, and professional certifications alike.
Why the old playbook stopped working
The scale of the problem is now measurable, and it is large. Across 19,368 interviews, Fabric flagged 48% of candidates in technical roles for AI assistance, and 61.1% of flagged candidates scored high enough to advance without a separate cheating check. Separately, 88% of online exams and assessments face AI cheating risk, and cheating and fraud attempt rates on proctored assessments more than doubled from 16% to 35% in a year. See the full dataset in our AI Cheating Statistics 2026 report. In our Cornell pilot, 70% of devices carried a hidden AI overlay before the session was secured.
The economics explain the surge. A human proxy test-taker historically cost $900–$2,500 per exam depending on certification tier (CertWizard pricing), while a general-purpose AI subscription costs roughly $20 a month and covers unlimited exams. When the cost of cheating collapses by two orders of magnitude, volume follows.
The incumbent defenses were designed for an earlier threat model:
- Webcam and gaze proctoring watches the candidate. But submitting a prompt to a phone takes a two-second glance indistinguishable from checking the time, and an invisible AI overlay renders on the same screen the candidate is already looking at.
- Lockdown browsers restrict the exam window. But everything that matters now runs outside the browser, whether a helper process, an on-device LLM, or a second device.
- Behavioral AI detectors guess intent from behavior, and every guess is a flag a person has to review. The result is alert fatigue, not prevention.
Detection is a signature database racing a global open-source community. Every time a tool is fingerprinted, it is recompiled with a new name within days. Prevention takes the opposite approach, and that is what the methods below are built on. (For the underlying numbers, see our AI Cheating Statistics 2026 report and the quarterly Threat Index.)
The three layers of assessment security
Every assessment-security stack has three layers. Understanding which layer a control lives in tells you exactly what it can and cannot stop.
- Physical / behavioral layer: webcams, gaze tracking, human review. Good for physical impersonation and out-of-frame anomalies; blind to anything on the device or invisible to the lens.
- Application / browser layer: lockdown and secure browsers. Good for other tabs and clipboard paste; blind to anything running outside the browser.
- Device + network layer: enforcement at the operating system and network stack. This is where 2026-era AI cheating actually happens, and the layer no incumbent was built to defend. It is the layer Aiseptor operates in.
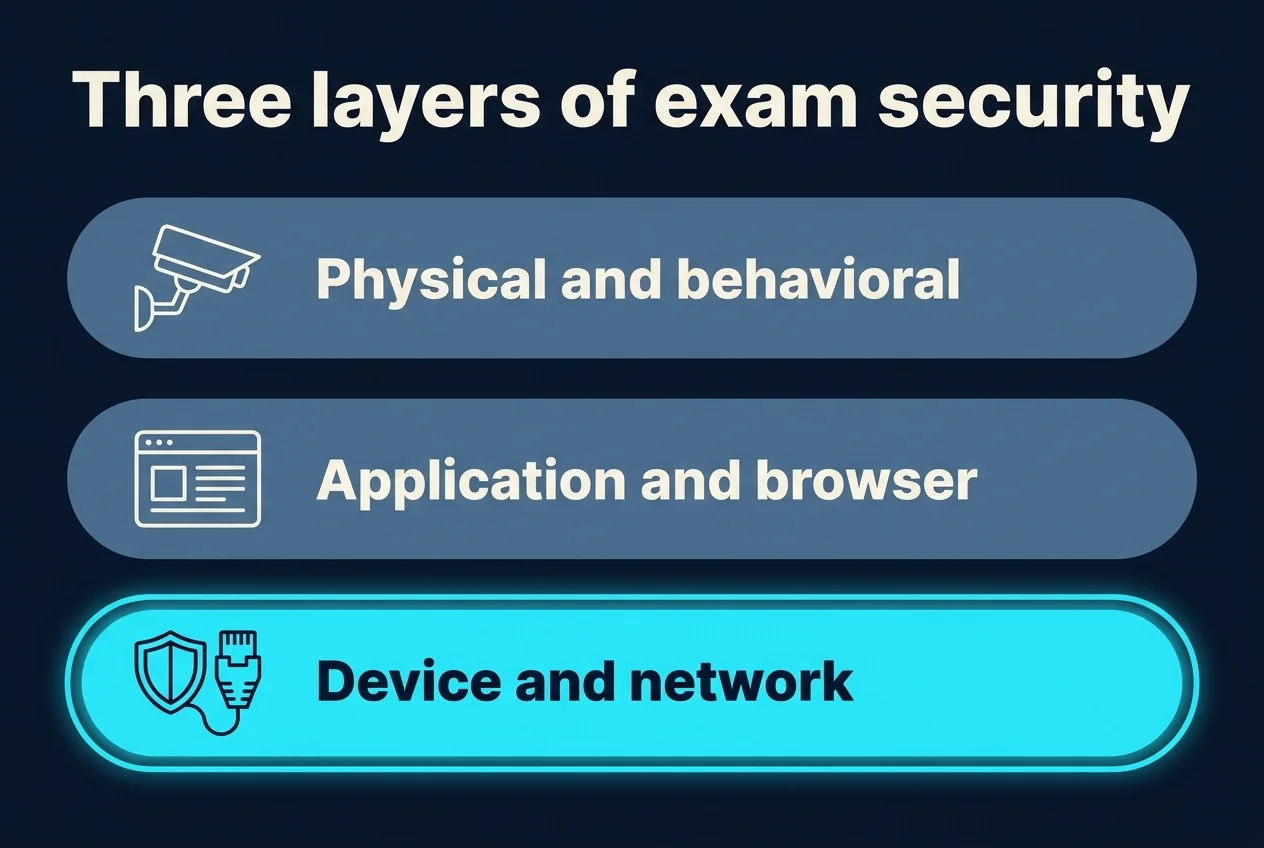
The methods that follow are how you defend the layer that matters. Most of them work at the device-and-network layer, plus the pairing controls that close the remaining gaps.
12 methods to prevent AI cheating in online assessments
1. Enforce a default-deny network policy per session
Start from the position that nothing is reachable unless the exam explicitly allows it. A default-deny architecture inverts the detection problem: instead of maintaining an ever-growing blocklist of AI tools, you maintain a short allowlist of what the assessment legitimately needs. Every other destination, including every AI inference endpoint, is dropped by default. This single control neutralizes the majority of cloud-based AI cheating regardless of the tool's name or UI.
2. Block AI inference endpoints at the network layer
Cloud AI assistance ultimately resolves to a request to a provider API. Blocking traffic to those endpoints, along with the DNS lookups that precede them, stops the overlay or chatbot from ever receiving an answer. Because DNS resolution happens before encryption, it is the earliest and cheapest point of interception. An overlay that cannot reach a model API is inert.
3. Cover every network interface, not just the primary one
A control that only watches the main connection is bypassed by a mobile hotspot or a tethered phone. Effective prevention applies the session policy across all interfaces on the device, so a second connection cannot become an unmonitored tunnel to an AI service.
4. Detect and block on-device LLMs
A locally run model (Ollama, LM Studio, local GGUF files) generates no external API traffic, so network blocking alone won't catch it. Prevention here means OS-level signals: active local-inference processes, model-hosting services, and the model-update endpoints those tools phone home to. This is the fastest-growing evasion path and the one camera proctoring and lockdown browsers cannot see at all.
5. Neutralize invisible AI overlays by their dependency, not their name
Tools like Cluely, OpenCluely, and Parakeet draw answers directly on screen and exclude themselves from screenshots. Process-name and screenshot-hash detection fails the moment the binary is renamed. The durable method is to block the overlay's network path to its inference endpoint and pair it with OS signals (screen-capture-exclusion flags, GPU/process activity). Whatever it's called, it's useless if it can't reach a model.
6. Block remote-access and screen-share pivots
Remote-control tools (AnyDesk, TeamViewer, Chrome Remote Desktop) and conferencing screen-shares (Discord, Zoom, Teams) let an off-screen helper see the exam and feed answers. Their relay and control servers are blocked at the session boundary, so a remote operator can't reach the device and a local agent can't phone home.
7. Flag virtual machines and second-screen output
Hardened anti-detection VMs and HDMI/wireless-mirroring outputs move exam content somewhere the controls don't watch. Surfacing virtualization artifacts and blocking virtual/extended display outputs forces these high-effort evasions into manual review instead of letting them pass silently.
8. Make the audit trail tamper-evident
A clean session log is trivial to fabricate. Require a cryptographically signed, per-session audit trail of every blocked attempt and integrity signal. This is what converts "no violations recorded" into evidence you can actually defend when a credential or hire is challenged.
9. Prefer prevention over post-hoc detection
Detection flags after the candidate may have already finished; prevention stops the action in real time and produces zero false positives because it is deterministic: it blocks a destination, it doesn't guess at intent. Deterministic prevention also avoids the bias and dispute problems that come with behavioral scoring.
10. Protect candidate privacy to reduce bias and disputes
You do not need to surveil a candidate to secure a session. Network-layer enforcement uses no webcam, no microphone, no keystroke logging, and no screen recording, and captures no footage at all, so there is none to retain. Less personal data collected means fewer privacy objections, less bias exposure, and fewer contested results, without weakening security.
11. Keep candidate friction low
A control that requires a kernel driver or a permanent install creates support tickets and abandonment, and pushes organizations back toward expensive in-person testing. An ephemeral, user-space enclave that deploys in under 10 seconds and removes itself at session end secures BYOD / unmanaged devices without leaving anything behind.
12. Layer network-layer prevention with physical proctoring where stakes demand it
Network-layer enforcement does not stop pen-and-paper notes or physical impersonation; those are the camera's job. For the highest-stakes exams, pair network-layer prevention (for the device/AI threats) with behavioral proctoring (for the physical ones). The layers are complementary, not competing.
Applying this to your assessment type
Online exams (academic & K-12)
Academic exams are high-volume and privacy-sensitive, which makes camera-only approaches both costly and contentious. Lead with network-layer enforcement to block AI overlays and on-device models, add behavioral proctoring only for the highest-stakes sittings, and keep retention short to satisfy student-privacy requirements.
Technical hiring & coding interviews
This is where AI cheating is most prevalent: nearly half of technical candidates are flagged. The exposure is invisible coding-assistant overlays and second devices during live or take-home assessments. Whitelist only the coding platform and approved docs, and block everything else, so candidates are evaluated on their own ability. See Aiseptor for platforms (Codility, HackerRank, CodeSignal-style integrations) and for enterprise hiring teams.
Professional certifications
Certification fraud scales through proxy rings and pay-after-pass services, and the move to remote delivery removed the test center's controls. A per-session enclave with a signed audit trail restores test-center-grade assurance without physical centers, and the tamper-evident record is what makes the credential verifiable downstream.
What to require when you evaluate a solution
Use this checklist when comparing vendors. The questions separate AI-era prevention from tools retrofit to mention it:
- Where does enforcement run: inside the browser, or at the OS and network layer?
- Is it default-deny, or does it rely on a blocklist of known AI tools?
- Does it monitor DNS and block AI inference endpoints before a connection completes?
- Can it detect on-device LLMs that produce no external traffic?
- Does it cover all network interfaces, including hotspots and VPNs?
- Is the audit trail cryptographically signed and tamper-evident?
- What does it collect, and can it work without webcam, microphone, or keystroke logging?
- What's the candidate footprint: a kernel driver and a permanent install, or an ephemeral user-space agent that removes itself?
If you're replacing or augmenting an incumbent, our alternatives comparisons walk through how network-layer enforcement maps against lockdown browsers and Safe Exam Browser.
The bottom line
AI-assisted cheating is not a harder version of the old cheating problem. It is a different problem at a different layer. Webcam proctoring and lockdown browsers still do what they were built to do, but the modern attacker operates beneath both. The organizations keeping assessments valid in 2026 are the ones that moved enforcement to the device and network layer, blocked the path instead of chasing the tool, and stopped collecting more candidate data than security actually requires.
Frequently Asked Questions
How do I stop candidates cheating on online assessments?
Start with what the cheating needs. Block every destination the exam does not need, so AI services and remote-access relays cannot be reached. Catch local models by their GPU memory and hidden overlays by their screen-capture-exclusion flag. Then add assessment design and human review for what software cannot see, like a person in the room.
How do you block AI during an online test?
Apply a default-deny network policy to the exam device for the session, so only the exam platform and approved resources resolve. That stops hosted AI tools whatever they are called. A model running locally needs no network, so it has to be caught on the device instead.
Can proctoring software detect ChatGPT?
Browser-based proctoring sees ChatGPT only if the candidate opens it in a monitored tab. A desktop app, an overlay or a phone stays outside its view. Network enforcement on the exam device blocks ChatGPT's servers for the session, but a phone on its own cellular connection still needs room-level controls.
Aiseptor is the network-layer security platform that assessment providers embed to prevent AI cheating, blocking invisible AI overlays, remote-access tools, and on-device LLMs with an enclave that deploys in under 10 seconds, with no webcam and no kernel driver. See how it works → or try it free →.